|
| The Latest Red Piranha News | This month’s priorities: knowing what’s in the environment, how it connects, and how quickly teams can act on it.
Our November campaigns on VAPT, DISP, MDR and Critical Infrastructure Resilience address that from four angles. The Crystal Eye CMDB addresses it at the platform level.
Now expanded in Orchestrate, with Organisations, Racks, Devices, Connections, IPAM, VPN and Virtualisation available from the My Deployments menu.
Read on for the full announcement and our October recap.
|
Crystal Eye CMDB Expands in Orchestrate |  | Red Piranha is pleased to announce the latest enhancements to the Crystal Eye CMDB within Orchestrate, the first of several major updates designed to strengthen asset management, infrastructure visibility, and cyber resilience across IT and OT environments.
Modern organisations often struggle with fragmented visibility. Network teams, security teams, and IT departments each maintain their own records, while assets span physical sites, virtual environments, cloud services, remote users, and operational technology. This fragmentation makes it difficult to answer simple but critical questions: what assets exist, who owns them, where they are located, what they connect to, and what business or security impact would follow if they were compromised or unavailable.
The expanded CMDB experience is now available from the My Deployments menu and introduces new capabilities including Organisations, Racks, Devices, Connections, IP Address Management (IPAM), VPN, and Virtualisation. Together, these capabilities provide a coordinated and consolidated view of assets across departments and sites within Red Piranha's cybersecurity mesh architecture.
The Crystal Eye CMDB automatically builds and maintains a comprehensive inventory of Configuration Items (CIs) using data collected from Crystal Eye deployments. This includes discovered devices, interfaces, network relationships, vulnerability scan results, Software Bills of Materials (SBOMs), hardware lifecycle information, sites, manufacturers, and organisational ownership structures. Instead of requiring teams to reconcile spreadsheets, disconnected tools, or manually maintained asset registers, the CMDB creates a continuously updated source of truth that reflects what exists in the environment and how critical assets are connected and dependent on one another.
By linking assets directly to vulnerability management, the CMDB helps security teams prioritise remediation based on real operational context, not just severity scores. Teams can see which vulnerable systems support critical services, which are internet facing, which sit in sensitive network segments, and which dependencies could amplify the impact of an incident. This turns vulnerability data into actionable decisions and helps reduce the risk of focusing effort on low impact issues while critical exposure remains unaddressed.
The enhanced CMDB helps NetOps, SecOps, and IT teams move beyond traditional asset inventories by providing valuable operational context. Device and interface relationship mapping enables faster incident investigation, improved threat hunting, more effective change management, and better informed decision making during security incidents. New capabilities such as IP Address Management, VPN visibility, rack awareness, and virtualisation mapping further extend insight across both physical and virtual infrastructure, helping teams maintain operational control while reducing complexity.
For NetOps teams, this means clearer visibility into network topology, address allocation, connectivity, and infrastructure dependencies. For SecOps teams, it means faster incident scoping, more accurate impact assessment, and stronger context for threat hunting. For IT and governance teams, it means improved accountability, change control, compliance readiness, and a shared understanding of the environment across organisational boundaries.
As Adam Bennett, CEO of Red Piranha, explains:
"A Configuration Management Database (CMDB) plays a crucial role in both incident response and threat hunting because it provides the authoritative source of truth about what exists in your environment. That includes your assets, their configurations, relationships, and dependencies."
With the Crystal Eye CMDB, organisations can proactively manage, protect, and prioritise their most critical assets through a single platform that combines automated discovery, infrastructure intelligence, vulnerability context, security telemetry, and operational visibility. Delivered within the Crystal Eye cybersecurity mesh architecture, the CMDB helps break down silos between security, networking, and IT operations, giving teams the shared, current, and actionable view they need to reduce risk, respond faster, and make more confident decisions.
This release represents another step in Red Piranha's commitment to delivering a more integrated and actionable view of modern cyber and infrastructure environments.
| | Learn more - CMDB Enhancements Now Available in Orchestrate |
Crystal Eye 6.0 Platform Updates |  The latest Crystal Eye platform update strengthens network visibility, endpoint protection, reporting, and system reliability. New capabilities across DHCP, DNS, WAF, CEASR, High Availability, IDPS, and WireGuard provide administrators with greater control and improved troubleshooting across their environments.
Key Features:
- Support for DHCP custom option 160 using text values for compatible device provisioning.
- Updated DNS rebind protection for private and link-local networks.
- Improved DNS reporting and visibility.
- Top Requested URLs added to Web Application Firewall reports.
- Application allow-listing introduced in CEASR for stronger application access control.
- Expanded High Availability logs with clearer interface, service, and configuration event details.
- Corrected Advanced Firewall and IDPS rule ordering.
- Additional IDPS logging support for Telnet, BitTorrent DHT, PostgreSQL, IMAP, EtherNet/IP, NTP, and QUIC.
- Improved WireGuard connection behaviour and wireless interface visibility.
- Additional safeguards for Crystal Eye 5.5 to 6.0 upgrades.
DNS Upgrade Notice
The latest Crystal Eye platform update strengthens network visibility, endpoint protection, reporting, and system reliability. New capabilities across DHCP, DNS, WAF, CEASR, High Availability, IDPS, and WireGuard provide administrators with greater control and improved troubleshooting across their environments.
Support & End-of-Life Reminders
- The current supported version of Crystal Eye OS is 6.0.
- We recommend that all customers upgrade from Crystal Eye 5.5 to 6.0.
- Crystal Eye 5.0 has reached End-of-Life Support.
Support Contact
Red Piranha Forum
|
Service Spotlight: MDR for OT and Critical Infrastructure Resilience |  | Critical infrastructure and industrial environments face a growing convergence of IT and OT risk. Energy, utilities, manufacturing, transport, and other operational environments depend on systems that were often designed for availability and reliability first, not always for modern cyber threats. A compromise in these environments can affect safety, service continuity, regulatory obligations, and public confidence.
Red Piranha’s Managed Detection and Response (MDR) service provides 24/7 monitoring, threat intelligence, and response capability across endpoint, network, cloud, and OT environments. For OT and ICS/SCADA environments, Crystal Eye delivers Threat Detection, Investigation and Response across OT traffic, helping teams identify anomalies and contain threats quickly.
The service combines automated detection and triage with expert analyst oversight. This Human-Machine Teaming model reduces alert noise while ensuring that high-risk incidents receive the attention they require. MDR can support containment actions such as isolating endpoints, revoking credentials, or blocking lateral movement, while digital forensics and investigation capability helps teams understand root cause and attack progression.
Who it is for:
- Energy, utilities, mining, manufacturing, transport, and other critical infrastructure operators
- Organisations with IT/OT convergence or industrial control systems
- Teams that need 24/7 detection and response without building a full in-house SOC
- Organisations seeking stronger resilience, visibility, and incident readiness
Technical approach:
Red Piranha's Crystal Eye MDR brings together telemetry from TDIR, NDR, endpoint agents, threat intelligence, and automated response workflows. It is designed to provide full-spectrum visibility, accelerate triage, and enable rapid containment across distributed and hybrid environments.
Compliance and standards alignment:
MDR for OT and critical infrastructure can support alignment with Essential Eight, IEC 62443, DISP, ISO/IEC 27001, and sector-specific resilience and regulatory requirements. Framework applicability should be confirmed based on the organisation’s industry, systems, and regulatory obligations.
| | Learn more about MDR |
Red Piranha Events | October 2026: A Month of Industry Engagement
October was an active month for Red Piranha, with opportunities to connect with industry professionals, defence stakeholders, cybersecurity specialists and organisations across Australia's energy sector.
Through these engagements, our team continued conversations around cybersecurity challenges, critical infrastructure protection, defence readiness and the importance of strengthening security operations.
| | Land Forces 2026 | Melbourne | 6–8 October 2026 | 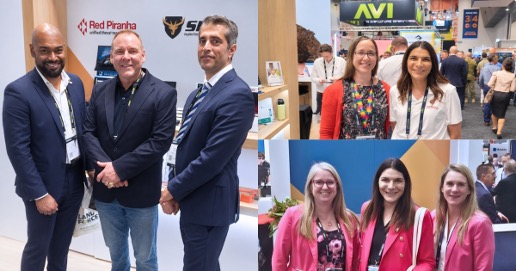 | Red Piranha participated in Land Forces 2026 in Melbourne, joining defence industry stakeholders, government representatives and technology providers for three days of engagement focused on Australia's defence capabilities and evolving security requirements.
Throughout the event, our team connected with organisations across the defence ecosystem to discuss cybersecurity priorities, supply chain security, DISP readiness and the protection of sensitive operational environments.
Discussions also highlighted the importance of cybersecurity capabilities that extend beyond conventional IT infrastructure, particularly as defence environments increasingly rely on interconnected systems, distributed operations and complex technology supply chains.
For organisations operating within or supporting the defence sector, maintaining visibility, managing vulnerabilities and strengthening security operations are important considerations in building a resilient defence ecosystem.
| | ACS Cybersecurity Forum | 16 October 2026 | 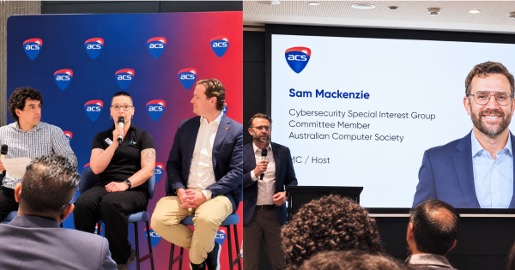 | Red Piranha joined cybersecurity professionals and industry leaders at the ACS Cybersecurity Forum to exchange perspectives on the challenges and priorities shaping Australia's cybersecurity landscape.
The engagement provided an opportunity to discuss emerging cyber threats, organisational resilience and the changing requirements facing Australian businesses as their technology environments become increasingly interconnected.
Conversations around security operations, threat visibility and incident response reinforced the importance of practical cybersecurity capabilities that help organisations identify potential weaknesses, understand their exposure and respond effectively to security incidents.
Events such as these also provide valuable opportunities for collaboration and knowledge sharing across Australia's cybersecurity community.
| | All Energy Australia 2026 | Melbourne | 28–30 October 2026 | 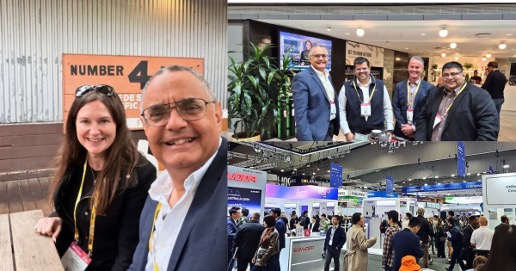 | Red Piranha attended All Energy Australia 2026 at the Melbourne Convention and Exhibition Centre (MCEC), connecting with organisations across the energy sector, industry stakeholders and supply chain partners.
Across three days, our representatives, George Boulis and Sameer Kalsi, engaged in discussions about the cybersecurity requirements of Australia's evolving energy landscape, including the protection of critical infrastructure, OT security and the importance of maintaining visibility across operational environments.
As energy infrastructure becomes increasingly connected, organisations need to understand the relationship between their IT and OT environments, identify unusual network activity and maintain appropriate security controls across critical systems.
Discussions throughout the event explored how advanced threat detection, incident response and security assurance can support energy-sector organisations in managing cyber risks while maintaining operational continuity.
For energy providers and their technology partners, cybersecurity is an important part of protecting infrastructure, supporting supply chain confidence, and maintaining the resilience of essential services.
|
|
|
|
| Copyright 2026 – Red Piranha - All Rights Reserved |
|
|
|