Threat Intelligence Report February 22nd - February 28th 2021
Trends
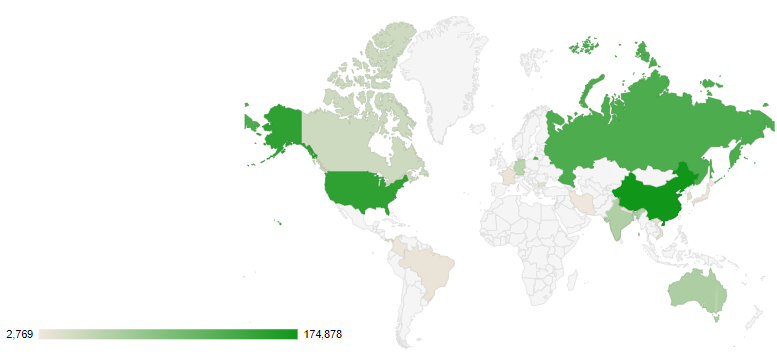
The top attacker country was China with 153498 unique attackers (59.66%).
The top Phishing campaign detected was against Facebook with 104 instances detected.
Once again, the importance of patching cannot be overemphasised. Four zero-day attacks were reported
by Microsoft, dubbed the Hafnium attacks. The attacks target the vulnerability on Microsoft Exchange servers by executing a server-side request forgery and remote code execution. Microsoft has released a patch for Exchange servers.
A previously identified bug, Spectre, was reported to be used as leverage to attack Windows, Linux,
Android, macOS and ChromeOS systems. The /etc/shadow file in Linux systems is used as leverage to
move laterally and dumped Kerberos tickets as leverage for an attack in Windows systems. The patch
has been available since the bug was identified. Details: CVE Identity is CVE 2017-5753
Default database credentials were used as leverage to steal personally identifiable information collected onto a database through logs generated by VPN apps for Android. Notably, the VPNs were possibly developed by the same person and carry the same features and utilise the same server. The solution to protecting one’s data when using a VPN would be to thoroughly assess the reviews to build trust in your
VPN provider.
A VMWare vulnerability was detected, which can be used by malicious actors to remotely upload
corrupted files and execute code in the logupload container. VMWare has provided a patch for this vulnerability. Details: CVE Identity-CVE-2021-21978 with CVSS score of 8.6 and severity rated as
Important.
Top Attackers By Country
Country
Occurences
Percentage
China
153498
59.66%
United States
59015
22.93%
Vietnam
8758
3.40%
Russia
6135
2.38%
Singapore
5877
2.28%
India
4408
1.71%
Philippines
2578
1.00%
Brazil
2520
0.97%
Bosnia and Herzegovina
2360
0.91%
Dominican Republic
2356
0.91%
Hong Kong
2196
0.85%
Taiwan
2134
0.82%
Tunisia
2046
0.79%
Thailand
1504
0.58%
Mexico
1290
0.50%
Algeria
591
0.22%
Top Attackers By Country
China
United States
Vietnam
Russia
Singapore
Others
Threat Geo-location
Top Attacking Hosts
Host
Occurrences
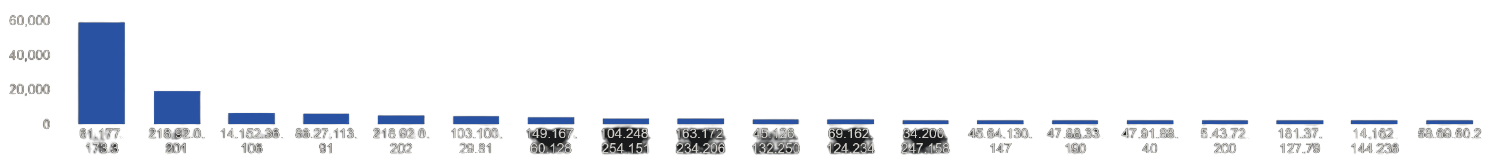
61.177.173.3
59219
218.92.0.201
19429
14.152.36.106
6624
86.27.113.91
6234
218.92.0.202
5144
103.100.29.81
5092
149.167.60.128
4237
104.248.254.151
3556
163.172.234.206
3379
45.126.132.250
2993
69.162.124.234
2807
34.200.247.158
2640
45.64.130.147
2488
47.88.33.190
2447
47.91.88.40
2440
5.43.72.200
2360
181.37.127.79
2356
14.162.144.236
2351
58.69.60.2
2348
Top Attackers
Top Network Attackers
ASN
Country
Name
4134
China
CHINANET-BACKBONE No.31,Jin-rong Street, CN
134764
China
CT-FOSHAN-IDC CHINANET Guangdong province network, CN
14061
United States
DIGITALOCEAN-ASN, US
12876
France
Online SAS, FR
132644
Indonesia
IDNIC-CBNCLOUD-AS-ID PT. Cyberindo Mega Persada, ID

 China
 United States
 Vietnam
 Russia
 Singapore
 Others